

[Feb-2022] CompTIA SY0-501 Dumps - Secret To Pass in First Attempt
CompTIA SY0-501 Exam Dumps [2022] Practice Valid Exam Dumps Question
NEW QUESTION 324
A company has a backup site with equipment on site without any data. This is an example of:
- A. a cold site.
- B. a warrn site.
- C. a hot standby.
- D. a hot site.
Answer: B
NEW QUESTION 325
A security consultant discovers that an organization is using the PCL protocol to print documents, utilizing the default driver and print settings. Which of the following is the MOST likely risk in this situation?
- A. An attacker can easily inject malicious code into the printer firmware.
- B. An attacker can access and change the printer configuration.
- C. SNMP data leaving the printer will not be properly encrypted.
- D. An MITM attack can reveal sensitive information.
- E. Attackers can use the PCL protocol to bypass the firewall of client computers.
Answer: C
NEW QUESTION 326
An organization wants to set up a wireless network in the most secure way. Budget is not a major consideration, and the organization is willing to accept some complexity when clients are connecting. It is also willing to deny wireless connectivity for clients who cannot be connected in the most secure manner. Which of the following would be the MOST secure setup that conforms to the organization's requirements?
- A. Enable WPA2-PSK, disable all other modes, and implement MAC filtering along with port security.
- B. Use WPA2-PSK with a 24-character complex password and change the password monthly.
- C. Use WPA2-Enterprise with RADIUS and disable pre-shared keys.
- D. Enable WPA2-PSK for older clients and WPA2-Enterprise for all other clients.
Answer: C
NEW QUESTION 327
Which of the following refers to applications and systems that are used within an organization without consent or approval?
- A. Insider threats
- B. Dark web
- C. OSINT
- D. Shadow IT
Answer: C
NEW QUESTION 328
Which of the following would a security specialist be able to determine upon examination of a server's
certificate?
- A. CSR
- B. Server private key
- C. OID
- D. CA public key
Answer: C
NEW QUESTION 329
Which of the following is the purpose of an industry-standard framework?
- A. To provide legal relief to participating organizations in the event of a security breach
- B. To promulgate security settings on a vendor-by-vendor basis
- C. To promulgate compliance requirements for sales of common IT systems
- D. To provide guidance across common system implementations
Answer: B
NEW QUESTION 330
DRAG DROP
A security administrator is given the security and availability profiles for servers that are being deployed.
Match each RAID type with the correct configuration and MINIMUM number of drives.
Review the server profiles and match them with the appropriate RAID type based on integrity, availability, I/O, storage requirements. Instructions:
All drive definitions can be dragged as many times as necessary
Not all placeholders may be filled in the RAID configuration boxes
If parity is required, please select the appropriate number of parity checkboxes Server profiles may be dragged only once Instructions: If at any time you would like to bring back the initial state of the simul-ation, please select the Reset button. When you have completed the simul-ation, please select the Done button to submit. Once the simul-ation is submitted, please select the Next button to continue.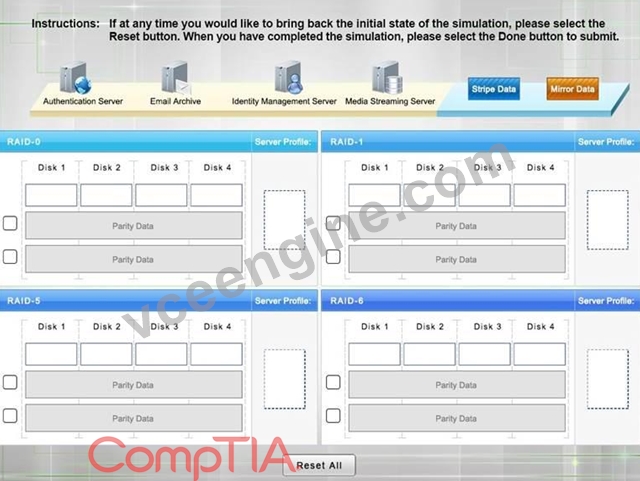
Answer:
Explanation:
Explanation:
RAID-0 is known as striping. It is not a fault tolerant solution but does improve disk performance for read/write operations. Striping requires a minimum of two disks and does not use parity. RAID-0 can be used where performance is required over fault tolerance, such as a media streaming server.
RAID-1 is known as mirroring because the same data is written to two disks so that the two disks have identical data. This is a fault tolerant solution that halves the storage space. A minimum of two disks are used in mirroring and does not use parity. RAID-1 can be used where fault tolerance is required over performance, such as on an authentication server.
RAID-5 is a fault tolerant solution that uses parity and striping. A minimum of three disks are required for RAID-5 with one disk's worth of space being used for parity information.
However, the parity information is distributed across all the disks. RAID-5 can recover from a sing disk failure.
RAID-6 is a fault tolerant solution that uses dual parity and striping. A minimum of four disks are required for RAID-6. Dual parity allows RAID-6 to recover from the simultaneous failure of up to two disks. Critical data should be stored on a RAID-6 system.
References:
Dulaney, Emmett and Chuck Eastton, CompTIA Security+ Study Guide, 6th Edition, Sybex, Indianapolis, 2014, pp. 34-36, 234-235
NEW QUESTION 331
The chief security officer (CS0) has issued a new policy that requires that all internal websites be configured for HTTPS traffic only. The network administrator has been tasked to update all internal sites without incurring additional costs.
Which of the following is the best solution for the network administrator to secure each internal website?
- A. Use a self-signed certificate on each internal server
- B. Use certificates signed by the company CA
- C. Use certificates signed by a public ca
- D. Use a signing certificate as a wild card certificate
Answer: A
Explanation:
Explanation
This is a way to update all internal sites without incurring additional costs?
To be a CA (Certificate Authority), you need an infrastructure that consists of considerable operational elements, hardware, software, policy frameworks and practice statements, auditing, security infrastructure and personnel.
NEW QUESTION 332
A network operations manager has added a second row of server racks in the datacenter.
These racks face the opposite direction of the first row of racks.
Which of the following is the reason the manager installed the racks this way?
- A. To eliminate the potential for electromagnetic interference
- B. To maximize fire suppression capabilities
- C. To lower energy consumption by sharing power outlets
- D. To create environmental hot and cold isles
Answer: D
NEW QUESTION 333
Task: Configure the firewall (fill out the table) to allow these four rules:
* Only allow the Accounting computer to have HTTPS access to the Administrative server.
* Only allow the HR computer to be able to communicate with the Server 2 System over SCP.
* Allow the IT computer to have access to both the Administrative Server 1 and Administrative Server 2

- A. See the solution below.
Use the following answer for this simulation task.
Below table has all the answers required for this question.
Firewall rules act like ACLs, and they are used to dictate what traffic can pass between the firewall and the internal network. Three possible actions can be taken based on the rule's criteria:
Block the connection Allow the connection
Allow the connection only if it is secured
TCP is responsible for providing a reliable, one-to-one, connection-oriented session. TCP establishes a connection and ensures that the other end receives any packets sent.
Two hosts communicate packet results with each other. TCP also ensures that packets are decoded and sequenced properly. This connection is persistent during the session.
When the session ends, the connection is torn down.
UDP provides an unreliable connectionless communication method between hosts.
The primary purpose of UDP is to send small packets of information.
The application is responsible for acknowledging the correct reception of the data. Port 22 is used by both SSH and SCP with UDP.
Port 443 is used for secure web connections? HTTPS and is a TCP port.
Thus to make sure only the Accounting computer has HTTPS access to the communication between 10.4.255.10/23 (HR) and 10.4.255.2 (server2)
Thus to make sure that the IT computer can access both the Administrative servers you need to use a port and accompanying port number and set the rule to allow communication between: 10.4.255.10.25 (IT computer) and 10.4.255.101 (Administrative server1)
10.4.255.10.25 (IT computer) and 10.4.255.102 (Administrative server2) - B. See the solution below.
Use the following answer for this simulation task.
Below table has all the answers required for this question.
Firewall rules act like ACLs, and they are used to dictate what traffic can pass between the firewall and the internal network. Three possible actions can be taken based on the rule's criteria:
Block the connection Allow the connection
Allow the connection only if it is secured
TCP is responsible for providing a reliable, one-to-one, connection-oriented session. TCP establishes a connection and ensures that the other end receives any packets sent.
Two hosts communicate packet results with each other. TCP also ensures that packets are decoded and sequenced properly. This connection is persistent during the session.
When the session ends, the connection is torn down.
UDP provides an unreliable connectionless communication method between hosts. UDP is considered a best-effort protocol, but it's considerably faster than TCP.
The sessions don't establish a synchronized session like the kind used in TCP, and UDP doesn't guarantee error-free communications.
The primary purpose of UDP is to send small packets of information.
The application is responsible for acknowledging the correct reception of the data. Port 22 is used by both SSH and SCP with UDP.
Port 443 is used for secure web connections? HTTPS and is a TCP port.
Thus to make sure only the Accounting computer has HTTPS access to the Administrative server you should use TCP port 443 and set the rule to allow communication between 10.4.255.10/24 (Accounting) and 10.4.255.101 (Administrative server1) Thus to make sure that only the HR computer has access to Server2 over SCP you need use of TCP port 22 and set the rule to allow communication between 10.4.255.10/23 (HR) and 10.4.255.2 (server2)
Thus to make sure that the IT computer can access both the Administrative servers you need to use a port and accompanying port number and set the rule to allow communication between: 10.4.255.10.25 (IT computer) and 10.4.255.101 (Administrative server1)
10.4.255.10.25 (IT computer) and 10.4.255.102 (Administrative server2)
Answer: B
NEW QUESTION 334
In a lessons learned report, it is suspected that a well-organized, well-funded, and extremely sophisticated group of attackers may have been responsible for a breach at a nuclear facility.
Which of the following describes the type of actors that may have been implicated?
- A. Competitor
- B. Insider
- C. Nation state
- D. Hacktivist
Answer: C
NEW QUESTION 335
Company A has acquired Company B. C
ompany A has different domains spread globally, and typically migrates its acquisitions infrastructure under its own domain infrastructure. Company B, however, cannot be merged into Company A's domain infrastructure.
Which of the following methods would allow the two companies to access one another's resources?
- A. Attestation
- B. Federation
- C. Single sign-on
- D. Kerberos
Answer: B
NEW QUESTION 336
A network administrator adds an ACL to allow only HTTPS connections form host 192.168.2.3 to web server 192.168.5.2. After applying the rule, the host is unable to access the server. The network administrator runs the output and notices the configuration below:
Which of the following rules would be BEST to resolve the issue?
A:
B:
C:
D:
- A. Option D
- B. Option C
- C. Option B
- D. Option A
Answer: D
NEW QUESTION 337
A state-sponsored threat actor has launched several successful attacks against a corporate network. Although the target has a robust patch management program in place, the attacks continue in depth and scope, and the security department has no idea how the attacks are able to gain access. Given that patch management and vulnerability scanners are being used, which of the following would be used to analyze the attack methodology?
- A. Rogue system detection
- B. Next-generation firewall
- C. Penetration test
- D. Honeypots
Answer: D
NEW QUESTION 338
A security analyst is testing both Windows and Linux systems for unauthorized DNS zone transfers within a LAN on comptia.org from example.org. Which of the following commands should the security analyst use? (Select two.)
- A. Option E
- B. Option C
- C. Option D
- D. Option F
- E. Option B
- F. Option A
Answer: B,F
NEW QUESTION 339
A systems administrator is attempting to recover from a catastrophic failure in the datacenter. To recover
the domain controller, the systems administrator needs to provide the domain administrator credentials.
Which of the following account types is the systems administrator using?
- A. User account
- B. Service account
- C. Shared account
- D. Guest account
Answer: A
NEW QUESTION 340
After attempting to harden a web server, a security analyst needs to determine if an application remains
vulnerable to SQL injection attacks.
Which of the following would BEST assist the analyst in making this determination?
- A. Nmap
- B. netcat
- C. nslookup
- D. tracert
- E. Fuzzer
Answer: E
NEW QUESTION 341
A user needs to send sensitive information to a colleague using PKI. Which of the following concepts apply when a sender encrypts the message hash with the sender's private key? (Select TWO)
- A. Steganography
- B. Transport security
- C. Message integrity
- D. Non-repudiation
- E. Email content encryption
Answer: C,D
NEW QUESTION 342
A company stores highly sensitive data files used by the accounting system on a server file share.
The accounting system uses a service account named accounting-svc to access the file share.
The data is protected will a full disk encryption, and the permissions are set as follows:
File system permissions: Users = Read Only
Share permission: accounting-svc = Read Only
Given the listed protections are in place and unchanged, to which of the following risks is the data still
subject?
- A. Remote exfiltration of data using domain credentials
- B. Theft of physical hard drives and a breach of confidentiality
- C. Disclosure of sensitive data to third parties due to excessive share permissions
- D. Exploitation of local console access and removal of data
Answer: D
NEW QUESTION 343
A company has three divisions, each with its own networks and services. The company decides to make its secure web portal accessible to all employees utilizing their existing usernames and passwords. The security administrator has elected to use SAML to support authentication. In this scenario, which of the following will occur when users try to authenticate to the portal? (Select two.)
- A. The portal will request an authentication ticket from each network that is transitively trusted.
- B. The back-end networks will request authentication tickets from the portal, which will act as the third- party service provider authentication store.
- C. The back-end networks will verify the assertion token issued by the portal functioning as the identity provider.
- D. The portal will function as a service provider and request an authentication assertion.
- E. The back-end networks will function as an identity provider and issue an authentication assertion.
- F. The portal will function as an identity provider and issue an authentication assertion.
Answer: D,F
NEW QUESTION 344
The availability of a system has been labeled as the highest priority. Which of the following should be focused on the MOST to ensure the objective?
- A. File integrity checking
- B. Authentication
- C. HVAC
- D. Full-disk encryption
Answer: C
NEW QUESTION 345
Confidential emails from an organization were posted to a website without the organization's knowledge. Upon investigation, it was determined that the emails were obtained from an internal actor who sniffed the emails in plain text.
Which of the following protocols, if properly implemented, would have MOST likely prevented the emails from being sniffed? (Choose two.)
- A. S/MIME
- B. Secure IMAP
- C. DNSSEC
- D. HTTPS
- E. SMTPS
Answer: A,E
NEW QUESTION 346
......
What's CompTIA SY0-501 Exam Outline?
The CompTIA SY0-501 exam content covers the following topics:
- Tools as well as Technologies (22%);
- Access Management and Identity (16%);
- Vulnerabilities, Threats, and Attacks (21%).
- Cryptography together with PKI (12%);
The CompTIA SY0-501 test consists of up to 90 questions and the students will have exactly 90 minutes to clear all of them. However, doing so may be a challenge even for an expert as the questions will be in multiple-choice and performance-based formats. The minimum passing score is 750 points (100-900). This exam can be taken in Simplified Chinese, Portuguese, Japanese, or English and costs $349 for US residents. Also, note that there is a newer version of this test available for taking, which has the same exam format and features but covers the advanced and updated content. It is coded, SY0-601, and starting November 12, 2020, will be launched to qualify students for the already mentioned CompTIA Security+ certification. For more information about this new exam and the entire Security+ learning path, you can visit the CompTIA website.
SY0-501 Exam Dumps PDF Guaranteed Success with Accurate & Updated Questions: https://www.vceengine.com/SY0-501-vce-test-engine.html
