Efficient study material
The questions in dump are designed by the professional experts, which cover a great many original questions from the real exams' dump. We offer 3 version of EC-Council Certified Security Analyst (ECSA) updated vce dumps to cater you need. Our advantage is to make you advanced to others.
Surely, if you are ambitious to achieve a good result in EC-Council Certified Security Analyst (ECSA) exam, you are expected to do sufficient practices. You, however, do really have little time for practices. We suggest that you should at least spend 20-30 minutes before exam. Short-term memory will help you a lot.
In the contemporary world, skill of computer become increasingly important, or may be crucial, which is more and more relevant to a great many industries. Priorities are always given to skillful computer operators, no matter in employment or promotion. EC-Council Certified Security Analyst (ECSA) certificate makes you advanced and competitive to others. However, do you really have any idea how to prepare for the EC-COUNCIL exam well? Don't worry. Our mission is to assist you to pass the EC-Council Certified Security Analyst (ECSA) actual test.

Excellent EC-Council Certified Security Analyst (ECSA) exam dumps
We are dedicated to study EC-Council Certified Security Analyst (ECSA) exam and candidates' psychology, and develop an excellent product, ECSAv8 test practice engine, to help our clients pass EC-Council Certified Security Analyst (ECSA) exam easily. EC-COUNCIL latest test engine accurately anticipates questions in the actual exam, which has a 98% to 100% hit rate. According to feedbacks of our clients, 99% of them passed EC-Council Certified Security Analyst (ECSA) exam. Therefore, there is no doubt that our product is high-quality and praised highly of, which makes us well-known in our industry. We can say immodestly that how lucky you are to notice our product and use it. You have already had high probabilities to pass EC-Council Certified Security Analyst (ECSA) exam.
Best wishes
Lastly, we sincerely hope that you can pass EC-COUNCIL EC-Council Certified Security Analyst (ECSA) actual exam test successfully and achieve an ideal marks.
After purchase, Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
High efficiency for preparation
We have done and will do a lot for your trust and consuming experience. Firstly, you can download demo in our website before you purchase it, which is a part of our EC-Council Certified Security Analyst (ECSA) complete dump. If you are content with our product, you can choose to buy our complete EC-Council Certified Security Analyst (ECSA) updated vce dumps. After your payment, we will send you a link for download in e-mail. Please note it after payment. All your information is rigorously confidential. You don't have to worry about your personal info will leak out. EC-COUNCIL practice test engine is updated according to the changes of EC-Council Certified Security Analyst (ECSA) actual exam, for the sake that the questions you practice are close to the real ECSAv8 exam, which enormously enhance your efficiency. Besides, our system will notify you automatically in e-mail if there is any update of EC-Council Certified Security Analyst (ECSA) vce torrent. What's more, if you unluckily were the 1% to fail, we could supply you a whole refund, you just need to show us your failed transcript. Lastly and most importantly, if you have any question during the whole section, no matter before sales of after sales, please contact us anytime. We set up a 24/7 customer service to settle all you problems about EC-Council Certified Security Analyst (ECSA) test study engine.
EC-COUNCIL ECSAv8 Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|
| Topic 1: Introduction to Security Analysis and Penetration Testing | 10% | - Penetration testing standards and frameworks
- Security assessment methodologies
|
| Topic 2: Malware Analysis and Reverse Engineering | 7% | - Static and dynamic malware analysis
- Reverse engineering fundamentals
|
| Topic 3: Cloud and Virtualization Security | 8% | - Virtual machine and hypervisor security
- Cloud infrastructure assessment
|
| Topic 4: Wireless and Mobile Security Assessment | 10% | - Wireless network encryption flaws
- Mobile device and application security analysis
|
| Topic 5: Web Application Security Assessment | 13% | - OWASP top 10 vulnerabilities
- Web application testing methodologies
|
| Topic 6: Information Gathering and Reconnaissance | 12% | - Network scanning and enumeration
- Active and passive reconnaissance
|
| Topic 7: Vulnerability Analysis and Assessment | 15% | - Vulnerability scanning tools and techniques
- Vulnerability classification and management
|
| Topic 8: Network Infrastructure Security Assessment | 15% | - Router, switch and firewall security testing
- IDS/IPS evasion and analysis
|
| Topic 9: Reporting and Documentation | 10% | - Risk rating and remediation recommendations
- Penetration test report structure
|
EC-COUNCIL EC-Council Certified Security Analyst (ECSA) Sample Questions:
DNS information records provide important data about:
- A. New Customer
- B. Phone and Fax Numbers
- C. Location and Type of Servers
- D. Agents Providing Service to Company Staff
Reveal Solution
Discussion
Identify the correct formula for Return on Investment (ROI).
- A. ROI = (Expected Returns Cost of Investment) / Cost of Investment
- B. ROI = ((Expected Returns + Cost of Investment) / Cost of Investment) * 100
- C. ROI = ((Expected Returns - Cost of Investment) / Cost of Investment) * 100
- D. ROI = (Expected Returns + Cost of Investment) / Cost of Investment
Reveal Solution
Discussion
Correct Answer: A 🗳️
Explanation: Only visible for VCEEngine members. You can sign-up / login (it's free).
Which of the following statement holds true for TCP Operation?
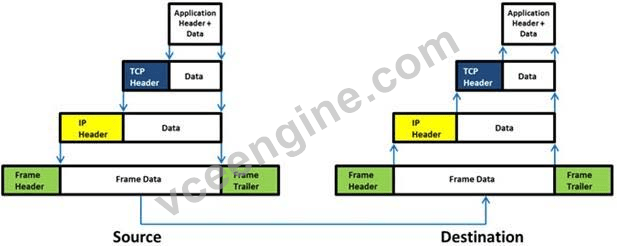
- A. Sequence numbers are used to track the number of packets lost in transmission
- B. Data transfer begins even before the connection is established
- C. Port numbers are used to know which application the receiving host should pass the data to
- D. Flow control shows the trend of a transmitting host overflowing the buffers in the receiving host
Reveal Solution
Discussion
Amazon Consulting Corporation provides penetration testing and managed security services to companies. Legality and regulatory compliance is one of the important components in conducting a successful security audit.
Before starting a test, one of the agreements both the parties need to sign relates to limitations, constraints, liabilities, code of conduct, and indemnification considerations between the parties.
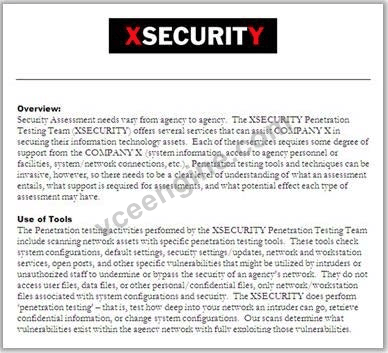
Which agreement requires a signature from both the parties (the penetration tester and the company)?
- A. Rules of engagement agreement
- B. Confidentiality agreement
- C. Non-disclosure agreement
- D. Client fees agreement
Reveal Solution
Discussion
What are placeholders (or markers) in an HTML document that the web server will dynamically replace with data just before sending the requested documents to a browser?
- A. Server Side Includes
- B. Sort Server Includes
- C. Server Sort Includes
- D. Slide Server Includes
Reveal Solution
Discussion


 Theresa

 Gavin

 Bonnie
 Nick
 Lyndon
 Claire
 Meredith

 Zora
 Reuben
 Zora
 Ansel
 Lesley
 Bartley
 Valerie
 Gloria
 Donahue
 Amy


